Skip to content

Strasbourg / Metz · In IT since 2017

Jean-Robert
Baehrel

Security & Infrastructure Engineer

Linux · DevSecOps · Vulnerability Intelligence · Agentic AI Security

I develop Resurgamus Horizon to manage secrets for infrastructure and AI agents, and CVE.radio to automate vulnerability intelligence.
Projects
Jean-Robert Baehrel
  • Operations and reliability
  • Infrastructure security
  • Development

Resurgamus Horizon

Open-source, self-hosted secrets management for infrastructure, CI/CD and AI agents. Access controls, auditability, cryptography and secure automation.

CVE.radio

Vulnerability intelligence and prioritization platform. KEV, EPSS, CVSS, exploitation signals and security automation.

01 / PROJECTS
Software I develop

Demo · synthetic data 1 / 14
Logo Resurgamus Horizon

Logo Resurgamus Horizon

Horizon interface with synthetic demonstration data.

Open demo ↗

reads/s

Secret reads under load

HA cluster, 10 workers, 32-core host with 64 GB RAM, PostgreSQL capped at 400 connections. No errors in these three measurements. The p99 latency is shown below each configuration.

1 client · 10 tokens 716 reads/s

p99: 118 ms

4 clients · 50 tokens 1,235 reads/s

p99: 290 ms

8 clients · 50 tokens 1,348 reads/s

p99: 290 ms

Source: Horizon capacity-planning documentation, HA cluster table; consulted on 4 November 2026.

View measurements and data
2024 - present Sole author and maintainer Beta open source

Resurgamus Horizon

Self-hosted secrets vault for AI agents and automation

I develop Horizon, a self-hosted secrets vault for AI agents, applications and CI/CD pipelines. Access is controlled through permissions, expiry and an audit trail. Its threat model assesses 43 ATT&CK techniques: 20 covered and 23 partially covered. The project includes an OWASP ASVS Level 2 assessment, a CRA requirements analysis and a build process with signatures, SBOMs and SLSA provenance. A Rust module protects keys in memory, and TLS connections support hybrid post-quantum key exchange.

Capacity benchmark: 1,348 secret reads/s, p99 290 ms

  • HA, failover and chaos testing on a multi-node cluster Load, failover and chaos tests on a multi-node cluster with PostgreSQL/Patroni. The capacity benchmark documents 1,348 secret reads/s, p99 latency of 290 ms and no errors at that load level. Separate tests measure median application failover of 27.47 s over 20 cycles and convergence in 2.1 s after key rotation.
  • Assessment of 43 ATT&CK techniques and OWASP ASVS requirements The model distinguishes 20 covered and 23 partially covered ATT&CK techniques, with their protections and limitations. The OWASP ASVS Level 2 assessment records 42 requirements met, one partial and two not applicable out of 45 examined.
  • Image verification with signatures, SBOMs and SLSA provenance Operators can verify image integrity and provenance and inspect the component list before deployment.
  • Python
  • Rust
  • FastAPI
  • PostgreSQL
  • Patroni
  • Docker
  • Kubernetes
  • Helm
CVE-2026-109618 · captured 5 Nov 20261 / 5
CVE-2026-109618 on CVE.radio, with CVSS, EPSS, KEV and patch badges.

A page for each vulnerability

Exploitation signals and update recommendations on the same page.

View the CVE page

events

Events tracked after publication

Events recorded as of 4 November 2026: an identified fix, an available PoC, addition to CISA KEV or a report of exploitation. One CVE may appear in several categories.

Fix identified 2,823 events
PoC available 833 events
Added to KEV 1,708 events
Exploitation reported 453 events

Source: CVE.radio cve_event snapshot, 4 November 2026. One record per CVE and event type. Dates come from source data or the first observation by CVE.radio.

View measurements and data
2026 - present Author and maintainer

CVE.radio

Vulnerability monitoring and prioritisation

CVE.radio collects vulnerability advisories and publishes a page for each CVE in French and English. It combines CERT-FR, CISA KEV, NVD, GitHub Advisories and Fortinet PSIRT with data from MITRE, OSV, FIRST and CIRCL. Each page lists affected products, available fixes and known signs of exploitation. Descriptions are translated with Mistral Small, then checked by a separate review model. AI analysis also assesses the likelihood of automated exploitation of a vulnerability.

  • Updating CVE pages as new events are reported Published CVEs continue to be updated from collected events. Readers can reassess priority and recommendations when new information becomes available.
  • Updating EPSS scores with each CVE collection run
  • Publishing CVE pages and JSON/XML feeds for monitoring tools
  • Python
  • SQLite
  • Docker
  • nginx
  • Varnish
  • Traefik
  • RSS
  • JSON
2026 - present Author and maintainer Alpha open source

Constellation

Asset and vulnerability exposure management (CAASM)

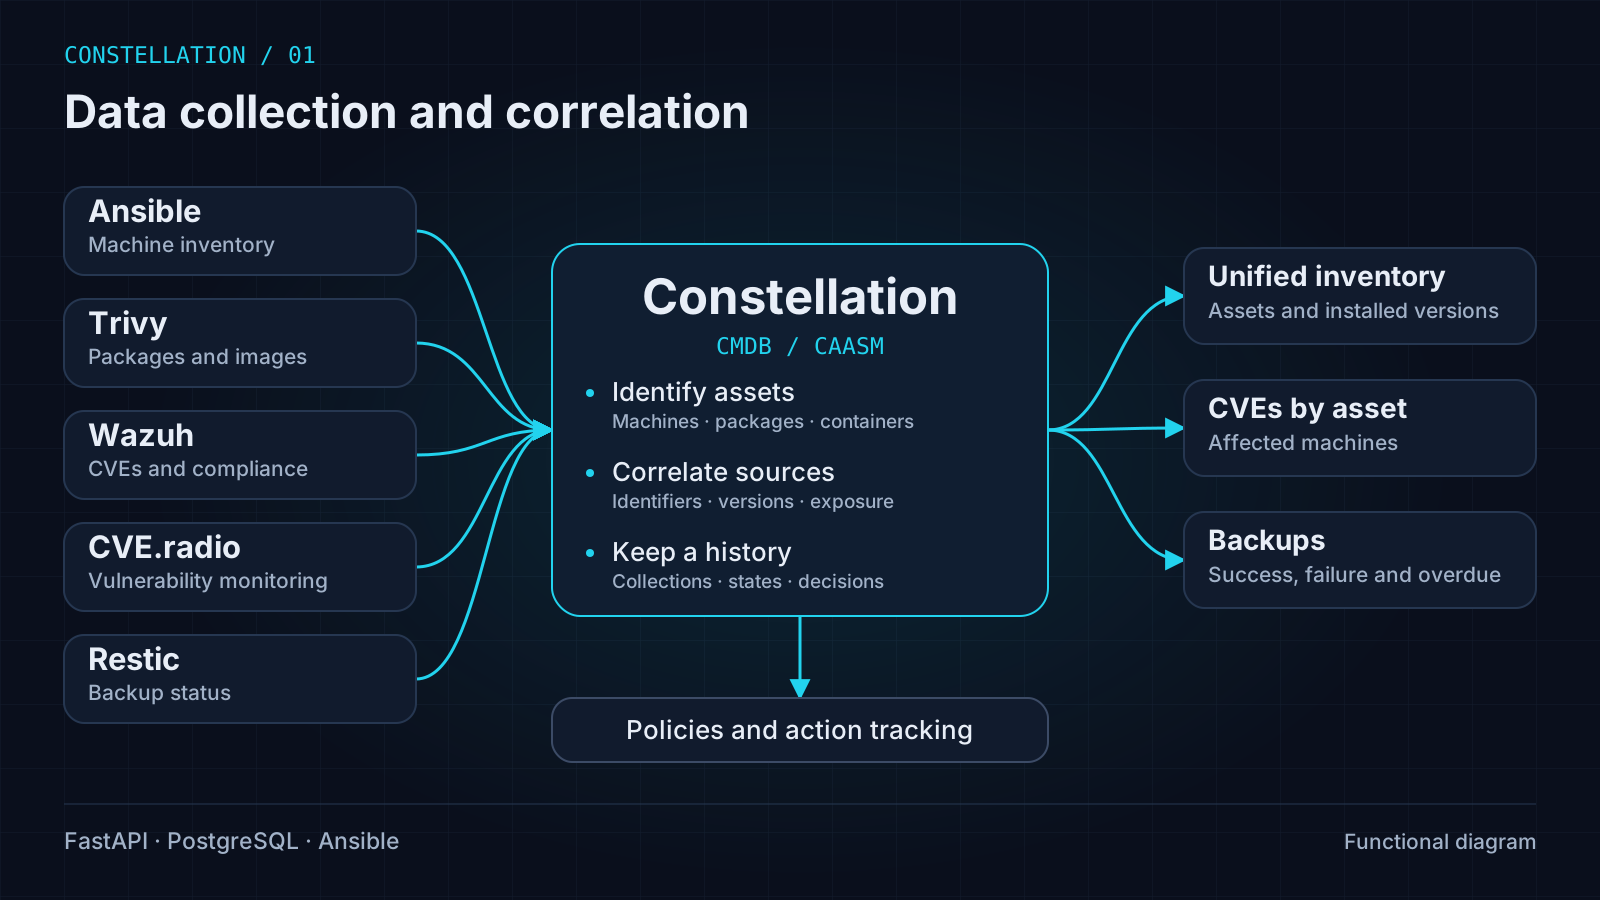
Constellation brings together asset inventory, vulnerabilities and backup status from Ansible, Trivy, Wazuh, Restic and CVE.radio. The project maps CVEs to affected machines and supports remediation through CI/CD pipelines or ticketing.

19 views and more than 76 API endpoints

  • Data collection from existing tools
  • Python dependencies hash-locked and audited in CI
  • Python
  • FastAPI
  • PostgreSQL
  • asyncpg
  • Ansible
  • Trivy
  • Wazuh
  • Restic

Other projects

  • pixelarray

    JavaScript library for pixel drawing on Canvas 2D

  • Resurgamus Backup

    Encrypted offsite backup platform for small businesses

  • Lich

    Design stage

    Monitoring and alerting server in Rust

02 / EXPERTISE

Systems, networks, security and governance

The systems and tools I use to administer, secure and automate infrastructure.

Operations and reliability

  • Incident response 9 yrs
  • Backup and recovery 9 yrs
  • Restic 9 yrs
  • Monitoring and observability 8 yrs
  • High availability 8 yrs
  • Service levels (SLA, SLO, SLI) 8 yrs
  • Database replication 8 yrs
  • Log analysis 8 yrs

Infrastructure security

  • System hardening 9 yrs
  • Security audit 9 yrs
  • VPN 9 yrs
  • BGP FlowSpec 7 yrs
  • DDoS protection 7 yrs
  • Firewall management 7 yrs
  • Fortinet FortiGate 7 yrs
  • IPsec 7 yrs

Development

  • Bash 9 yrs
  • JavaScript 9 yrs
  • Python 8 yrs
  • Application security 2 yrs
  • Access control and RBAC 2 yrs
  • Applied cryptography 2 yrs
  • API security 2 yrs
  • Rust 2 yrs

Governance

  • Technical documentation 9 yrs
  • Service levels (SLA, SLO, SLI) 8 yrs
  • RIPE NCC 7 yrs
  • Regulatory compliance 2 yrs
  • Crisis management

Security operations

  • Incident response 9 yrs
  • Bitdefender GravityZone 9 yrs
  • Wazuh 9 yrs
  • Log analysis 8 yrs
  • Compromise detection 7 yrs
  • HarfangLab 1 yr
  • Hornetsecurity 1 yr
  • Trellix ENS 1 yr

Automation

  • Ansible 9 yrs
  • CI/CD 8 yrs
  • GitLab 7 yrs
  • Toil reduction 2 yrs
  • Software supply chain security 2 yrs
  • OpenTofu / Terraform 2 yrs
  • AI agent automation (MCP) 2 yrs
  • LLM integration 1 yr

Years reflect my use of each skill in jobs and projects. Overlapping periods are counted once.

See all skills

03 / CAREER

My professional experience

My work in hosting, managed services and healthcare, alongside my freelance work.

Operations Administrator

Contract 2025 - present

ESN - Hospital sector, end client France

I operate and monitor hospital IT systems, handling system, network and security incidents in coordination with the SOC.

Environment: 18,000 users, 3,000 servers, 630 applications, 10,000 workstations

  • Nagios
  • HarfangLab
  • Trellix ENS
  • Hornetsecurity
  • MECM
  • VPN
  • Ansible

Infrastructure, security and digital projects consultant

Freelance 2017 - present

Resurgamus Informatique Strasbourg / Metz

I administer and secure IT infrastructure for small businesses and professional firms, and provide consulting and training.

  • Linux
  • Debian
  • Ansible
  • Docker
  • Postfix
  • Restic
  • Wazuh
  • OVHcloud

Systems Administrator L2/L3

Employee 2018 - 2025

SdV Plurimedia - Hosting and managed services provider Strasbourg

Operations and security for more than 1,000 servers, 24/7 L2/L3 on-call support, DDoS remediation and automation. Participation in steering committees for a major customer to review infrastructure, vulnerabilities, updates and action plans.

Environment: More than 1,000 production servers

  • Linux
  • Debian
  • Red Hat
  • Rocky Linux
  • CentOS
  • Docker
  • Kubernetes
  • Rancher

View all experience

04 / EDUCATION

Education and certifications

Certifications earned

  • 2020Cisco CCNA - Cisco (Cisco Certified Network Associate)
  • 2019ISC2 SSCP - ISC2 (Systems Security Certified Practitioner)
  • 2016CompTIA Linux+ (LPIC-1) - CompTIA / Linux Professional Institute

Education

  • 2017Web application developer - 3W Academy, Strasbourg (RNCP Bac+2)

Courses and additional training

  • 2026Introduction to the EBIOS Risk Manager method - Club EBIOS
  • 2025Bitdefender MSP Commercial 2023 - Bitdefender
  • 2025Bitdefender MSP Technical 2024 - Bitdefender
  • 2019MongoDB M001, M103, M201 - MongoDB University
  • 2019International Cyber Conflicts - SUNY, Coursera
  • 2019Cybersecurity for Business - University of Colorado, Coursera
  • 2018Ansible Essentials - Red Hat (Udemy)
  • 2018Deploying Containerized Applications - Red Hat (Udemy)
  • 2018RHEL Technical Overview - Red Hat (Udemy)
  • 2017The Complete Cyber Security Course, volumes 1 to 4 - Nathan House (Udemy)
  • 2016C programming - Pr Jacques Olivier Lapeyre

Training

  • 2026ISO 27001 Lead Implementer (ISO/IEC 27001) training completed

    Certification examination planned for late November 2026.
Languages

  • French - Native
  • English - Technical reading and writing
  • German - Basic

05 / CONTACT

Get in touch